To all the Beginners
The metamorphism into a hacker
Welcome to Hackthissite, a non-profit organization intended to teach you about computer security/hacking. Look around the site and you will find Missions to be completed and a well-maintained forum. Take time to read the articles available here and increase your repertoire of knowledge. Feel free to ask, and asking as a script kiddie is a skill in itself which I will cover later.
What is taught here
The main focus on Hackthissite is web hacking and exploitation. For this knowledge of HTML is necessary as it is the bread and butter of things to come. Take time to learn it here:
http://www.w3schools.com/
Have fun doing the challenges, have a determination to learn and you will become a great hacker in no time.
What about hacking in the movies
Movies such as Die Hard 4.0 show hacking as what most teenagers and villains do. This is entirely false as preteens as young as 12 learn and the majority of hackers are “White Hat”. This is a stereotype which many civilians believe hackers are.
Next is the “hacking part” in the movies. You hear them mention about Nmap and there is a certain program opened with black background and white text only with strange code on it. Now this is “Server Rooting,” a very advanced type of hacking. This is hacking into the server and exploitation of the operating system, which takes years of hacking to even get to the “newbie” part of it.
[u]How about the hacking programs online? Do they make me a hacker?[/u]
Most certainly not. There programs are made by hackers, obviously black hat, to infiltrate into the script kiddie community and wreck havoc. What you don’t know is that there may be a line of code in there which makes you contribute to a huge DOS attack.
A hacker can be defined as this:
http://www.catb.org/~esr/faqs/hacker-howto.html#attitude
A hacker hacks by exploiting code and hacks manually, not using the program of others. If he needs a program he shall program it himself.
[u]What programming language should I learn? Many people say that I shouldn’t start on BASIC but it’s so simple![/u]
I am a victim of the bad syntax of BASIC. Once you learn BASIC it is very hard to break the bad habit of its syntax. Especially a wide gap as switching from BASIC to C++. However this does not mean it’s a bad language. It still is a programming language but once you master BASIC you should stick to BASIC.
A better start would be Python, Perl or Ruby. These are also high-level programming languages such as BASIC but their syntax is much better. For seconds you should try C/C++. These are quite hard to learn for a beginner so you should master a simpler programming language first.
Why do I always get flamed on the forums when I ask them to hack a website for me? You told me that I should ask!
You were obviously asking wrongly. First here’s an introduction to the most-used forum rule:
Hackthissite shall not support illegal activities.
To ask smart and viable questions read this:
[url] http://catb.org/~esr/faqs/smart-questions.html#intro[/url]
Now a bad example would be:
Yooz peepz yuz gotza help me 2 hax0r tHis wak0 sitE.
A good example would be:
Hello there,
I’m really new to this site. Could you please kindly explain to me how this PHP exploitation works?
Thanks in advance,
-username here-
Now this is the way to ask smart questions. Don’t ask directly about hacking, just phrase it in an indirect way.
To the light side,
IncandescentLight
Showing posts with label hacking. Show all posts
Showing posts with label hacking. Show all posts
Sunday, March 8, 2009

Saturday, February 28, 2009
Web Hacking and Server Rooting
Web Hacking and Server Rooting
For many newcomers and beginners, your might be confused about the difference between web hacking and server rooting. They are both different things, and firstly I shall introduce you to web hacking.
Web hacking
What is web hacking? It is the exploitation of vulnerabilities within a website to deface it or gain root access of the site. A prime example is the basic and realistic missions on hackthissite.
Example 1:
Bob finds a website he doesn’t like, www.website.com . He does a routine search and finds an improperly configured .htaccess file that leads him to be able to access the /haccess area.
After finding the password from the admin/.hpasswd area he realizes it is a hash. He opens up John the Ripper, cracks the hash and gains access to the website.
Example 2:
Bob finds another website, and he wishes to deface it. He finds a comment area, and finds it is vulnerable to directory transversals. So he sets the comment name to go back 2 directories to the index.php page and inputs the defacing code he wants.
Server rooting
This is the kind of hacking you see in movies involving Nmap, Backtrack and the “Black and white command prompt screen with strange code.” Unfortunately I have very little experience in rooting as HackThisSite teaches only web hacking. This type of hacking is also much more difficult because it involves exploiting vulnerabilities in the operating system.
Example 1:
Bob finds a website. He does a port scan of it and finds the telnet port open, port 23. He brings up the command prompt and inputs in the command:
telnet www.somewebsite.com 23.
He then exploits a vulnerability in the operating system which leads him to an Administrator account with full privileges.
Know you know,
IncandescentLight
For many newcomers and beginners, your might be confused about the difference between web hacking and server rooting. They are both different things, and firstly I shall introduce you to web hacking.
Web hacking
What is web hacking? It is the exploitation of vulnerabilities within a website to deface it or gain root access of the site. A prime example is the basic and realistic missions on hackthissite.
Example 1:
Bob finds a website he doesn’t like, www.website.com . He does a routine search and finds an improperly configured .htaccess file that leads him to be able to access the /haccess area.
After finding the password from the admin/.hpasswd area he realizes it is a hash. He opens up John the Ripper, cracks the hash and gains access to the website.
Example 2:
Bob finds another website, and he wishes to deface it. He finds a comment area, and finds it is vulnerable to directory transversals. So he sets the comment name to go back 2 directories to the index.php page and inputs the defacing code he wants.
Server rooting
This is the kind of hacking you see in movies involving Nmap, Backtrack and the “Black and white command prompt screen with strange code.” Unfortunately I have very little experience in rooting as HackThisSite teaches only web hacking. This type of hacking is also much more difficult because it involves exploiting vulnerabilities in the operating system.
Example 1:
Bob finds a website. He does a port scan of it and finds the telnet port open, port 23. He brings up the command prompt and inputs in the command:
telnet www.somewebsite.com 23.
He then exploits a vulnerability in the operating system which leads him to an Administrator account with full privileges.
Know you know,
IncandescentLight
Saturday, January 24, 2009
Instant Messenger hacking
There can be many hectic things online such as rampaging perverts, spammers and script kiddies on instant messaging programs. It would be good, then, to learn a self-defence method I am going to teach you. This is a Denial of Service method which will disconnect or badly lag your opponent if used.
First thing is to understand how your text messages are sent to your messaging partner. In MSN messenger and Yahoo they are using an old method of instant messaging, which looks something like this.
Your computer->MSN/Yahoo IM server->Friend’s computer
This is like a relay, in which athletes pass the baton to they’re team members to complete the race. However, this is usually the slower method compared to direct sending, such as Skype, and it is harder to extract the IP this way.
MSN/Yahoo messengers, however, allow a direct connection if a file, being larger than 1 MB, is sent. This is so that they’re servers don’t lag up. So the connection would look something like this:
Your computer->Friend’s computer
And also this direct connection is faster. So we start up command prompt (Run>cmd) and enter the command netstat. This is a command used to find all the active connections to the computer. So to avoid complication, close down all other internet connections except the Instant Messenger. Then, send him/her any file which is larger than 1 MB. After he accepts it, enter the netstat command into command prompt and search for his IP. It should be the odd one out of all the connections, plausibly and FTP type connection or the odd-one-out IP.
After obtaining your victim’s IP address, you can write your own script or download one of my programs which I wrote from here:
http://www.filefactory.com/file/a0361gc/n/Pinger_zip
Extract it and enter the IP you wish to DOS and also the payload.
The DOS attacks heavily rely on your bandwidth as I have mentioned in my previous article here, http://www.hackthissite.org/articles/read/1016.
First thing is to understand how your text messages are sent to your messaging partner. In MSN messenger and Yahoo they are using an old method of instant messaging, which looks something like this.
Your computer->MSN/Yahoo IM server->Friend’s computer
This is like a relay, in which athletes pass the baton to they’re team members to complete the race. However, this is usually the slower method compared to direct sending, such as Skype, and it is harder to extract the IP this way.
MSN/Yahoo messengers, however, allow a direct connection if a file, being larger than 1 MB, is sent. This is so that they’re servers don’t lag up. So the connection would look something like this:
Your computer->Friend’s computer
And also this direct connection is faster. So we start up command prompt (Run>cmd) and enter the command netstat. This is a command used to find all the active connections to the computer. So to avoid complication, close down all other internet connections except the Instant Messenger. Then, send him/her any file which is larger than 1 MB. After he accepts it, enter the netstat command into command prompt and search for his IP. It should be the odd one out of all the connections, plausibly and FTP type connection or the odd-one-out IP.
After obtaining your victim’s IP address, you can write your own script or download one of my programs which I wrote from here:
http://www.filefactory.com/file/a0361gc/n/Pinger_zip
Extract it and enter the IP you wish to DOS and also the payload.
The DOS attacks heavily rely on your bandwidth as I have mentioned in my previous article here, http://www.hackthissite.org/articles/read/1016.
Wednesday, January 7, 2009
DOS attacks
DOS (Denial of Service) attacks, heard of them taking down servers, restricting traffic and even bringing down a country's communications. But, how do they work? A simple example would that being a heart. Let’s say the veins are the internet. And you are pumping blood through this tube. The blood is good traffic. What happens if you overload the veins with fat (bad traffic)? And so the heart has a failure and can’t pump blood to the other organs, a Denial of Service.
DOS attacks are one of the simplest ways to bring down a server, by overwhelming its bandwidth or computing resources. A simple DOS attack code would be:
ping {ip} -t -l 50000
In which you can just enter into the command prompt. This command sends 50000 bytes (roughly 50 kilobytes) of data to the ip, in a single packet. The -t is to ping the specified host until stopped and -l is to specify the buffer size. DOS are commonly used by script kiddies.
However, DOS attacks may crash systems by overloading their computing resources like having a heart attack. Sooner or later you have to get to a doctor or die (no offense meant). This only works in older systems due to the tremendous increase in computing power.
To prevail in a DOS attack, however, the attacker's bandwidth must be wider than the defender's bandwidth to overwhelm it with traffic, so more fat can get to the heart. This is only for singular attacks only (one on one). However, in a DDOS(Distributed Denial of Service) attack, the attacker may use zombie computers to send packets to the victim, therefore intensifying the attack. Imagine a huge clog with more than a few hundred computers streaming it.
Instead of using zombie computers, attackers may also choose to spoof their ips to that of their victim's computer. By doing so, he can send ip packets to many computers, and so the computers respond in pinging to the sender's ip. However, the sender's ip has been spoofed and so they unknowingly flood the victim. This is known as a Reflected attack.
DOS attacks can be so harmful that they may cause system damage in which the system is attacked so badly when they exploit flaws in the system, and then 'update' the device to modify it to make it permanently unusable.
DOS defense tactics
Firewalls provide protection from some DOS attacks by differentiating good traffic from DOS attacks but however a more complex attack on port 80 would have the server fully vulnerable because it is the web service port. Another way is the ISP(Internet Service Provider) noticing the attack and disconnecting the attacker.
Rerouting traffic through routers to auxiliary servers to help in filtering the bad traffic from good traffic also helps as it weighs less strain on the main server and allocates computing resources. Another way is to hide the host. The best foolproof way, however, is to plug out the internet cable and wait it out.
DOS attack tools:
FATA-jack
HyperWRT
MDK2
Recent famous DOS attacks include:
The DOS attack of Georgia weeks after the Russian-Georgian war. This caused multiple Georgian servers to be shut down and overloaded communications.
In July 2008 4chan received a 10gbps attack and suffered 2 weeks of downtime.
In September 2008 Digg and Gamesurge went under heavy DOS attacks and became offline for 6 hours.
Peace out,
IncandescentLight
*This article was also published in hackthissite under my user IncandescentLight
DOS attacks are one of the simplest ways to bring down a server, by overwhelming its bandwidth or computing resources. A simple DOS attack code would be:
ping {ip} -t -l 50000
In which you can just enter into the command prompt. This command sends 50000 bytes (roughly 50 kilobytes) of data to the ip, in a single packet. The -t is to ping the specified host until stopped and -l is to specify the buffer size. DOS are commonly used by script kiddies.
However, DOS attacks may crash systems by overloading their computing resources like having a heart attack. Sooner or later you have to get to a doctor or die (no offense meant). This only works in older systems due to the tremendous increase in computing power.
To prevail in a DOS attack, however, the attacker's bandwidth must be wider than the defender's bandwidth to overwhelm it with traffic, so more fat can get to the heart. This is only for singular attacks only (one on one). However, in a DDOS(Distributed Denial of Service) attack, the attacker may use zombie computers to send packets to the victim, therefore intensifying the attack. Imagine a huge clog with more than a few hundred computers streaming it.
Instead of using zombie computers, attackers may also choose to spoof their ips to that of their victim's computer. By doing so, he can send ip packets to many computers, and so the computers respond in pinging to the sender's ip. However, the sender's ip has been spoofed and so they unknowingly flood the victim. This is known as a Reflected attack.
DOS attacks can be so harmful that they may cause system damage in which the system is attacked so badly when they exploit flaws in the system, and then 'update' the device to modify it to make it permanently unusable.
DOS defense tactics
Firewalls provide protection from some DOS attacks by differentiating good traffic from DOS attacks but however a more complex attack on port 80 would have the server fully vulnerable because it is the web service port. Another way is the ISP(Internet Service Provider) noticing the attack and disconnecting the attacker.
Rerouting traffic through routers to auxiliary servers to help in filtering the bad traffic from good traffic also helps as it weighs less strain on the main server and allocates computing resources. Another way is to hide the host. The best foolproof way, however, is to plug out the internet cable and wait it out.
DOS attack tools:
FATA-jack
HyperWRT
MDK2
Recent famous DOS attacks include:
The DOS attack of Georgia weeks after the Russian-Georgian war. This caused multiple Georgian servers to be shut down and overloaded communications.
In July 2008 4chan received a 10gbps attack and suffered 2 weeks of downtime.
In September 2008 Digg and Gamesurge went under heavy DOS attacks and became offline for 6 hours.
Peace out,
IncandescentLight
*This article was also published in hackthissite under my user IncandescentLight
Saturday, August 2, 2008
Hacthissite Basic missions
Hackthissite Basic 1
After you learned HTML, view the source. In a comment will be the password for this level. To view the source wight-click the page and select view source or ViewSource on you menu bar. Press CTRL+F in the source and find 'password is' without the quotation marks.
Hackthissite Basic 2
'However, he neglected to upload the password file...'
So since there is no file it will be reffered to as nothing so just hit the submit button without typing anything.
Hackthissite Basic 3
Now look in the source code. You will find:
Paste password.php in your URL bar with so it is http://www.hackthissite.org/missions/basic/3/password.php and that is where the password is.
Hackthissite Basic 4
Again, look in the source code. You will find " input type="hidden" name="to" value="webmaster@hulla-balloo.com"> ". Now just change the value to your email, save as .HTML and click the button!
Hackthisste Basic 5
Paste javascript:alert( document.forms[0].to.value = youremail@youremail.org). This is a javascript injection which will alter the hidden fields of a page.
Hackthissite Basic 6
This site will help you. http://www.asciitable.com/. What you need to know is that for every new space the ascii value will be n+1, n being the ascii value added to the previous one.
Hackthissite Basic 7
Now, research unix commands. The most likely would be "ls". Now, how do you input two unix commands in one command line? Paste "&& ls" into the the box, locate the file and view it.
Hackthissite Basic 8
Paste into the name box and hit enter. Thi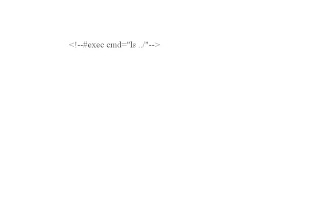 s is an SSI command which will instruct the server to show all the files.
Hackthissite Basic 9
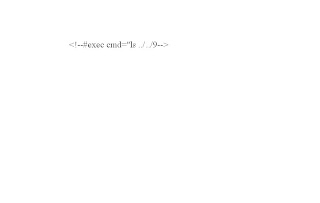 Paste into the submit box in the Basic 8 mission. This will search for the file in the Basic 9 directory.
After you learned HTML, view the source. In a comment will be the password for this level. To view the source wight-click the page and select view source or ViewSource on you menu bar. Press CTRL+F in the source and find 'password is' without the quotation marks.
Hackthissite Basic 2
'However, he neglected to upload the password file...'
So since there is no file it will be reffered to as nothing so just hit the submit button without typing anything.
Hackthissite Basic 3
Now look in the source code. You will find:
Paste password.php in your URL bar with so it is http://www.hackthissite.org/missions/basic/3/password.php and that is where the password is.
Hackthissite Basic 4
Again, look in the source code. You will find " input type="hidden" name="to" value="webmaster@hulla-balloo.com"> ". Now just change the value to your email, save as .HTML and click the button!
Hackthisste Basic 5
Paste javascript:alert( document.forms[0].to.value = youremail@youremail.org). This is a javascript injection which will alter the hidden fields of a page.
Hackthissite Basic 6
This site will help you. http://www.asciitable.com/. What you need to know is that for every new space the ascii value will be n+1, n being the ascii value added to the previous one.
Hackthissite Basic 7
Now, research unix commands. The most likely would be "ls". Now, how do you input two unix commands in one command line? Paste "&& ls" into the the box, locate the file and view it.
Hackthissite Basic 8
Paste into the name box and hit enter. Thi
 s is an SSI command which will instruct the server to show all the files.
Hackthissite Basic 9
 Paste into the submit box in the Basic 8 mission. This will search for the file in the Basic 9 directory.
Hackthissite Basic 10
Ahh, editing cookies. Use this javascript injection: javascript:void(document.cookie="level10_authorized=yes") to edit the cookies. Paste the javascript injection in the URL bar.
Ahh, editing cookies. Use this javascript injection: javascript:void(document.cookie="level10_authorized=yes") to edit the cookies. Paste the javascript injection in the URL bar.
Friday, August 1, 2008
Hello World!
Hello, I've just tried blogging for a pastime and I'm finding it reasonably easy. I hope to share my thoughts and opinions on several things through this blog. In computer languages, I'm fluent in HTML, Basic and C++. I have been interested in computers all my life and since last year i have been excessively mastering my computing skills. I also like playing chess, basketball and spend most of my pastimes in recreation.
I have created a few programs in C++ and Basic, in which i will have a download section on available soon. These contain either mathematical programs or trojans.
I will define in a few later posts the art of hacking through web attacking, which I hope you will all enjoy.
I have created a few programs in C++ and Basic, in which i will have a download section on available soon. These contain either mathematical programs or trojans.
I will define in a few later posts the art of hacking through web attacking, which I hope you will all enjoy.
Subscribe to:
Posts (Atom)

